Breach confirmed in KepcoON platform and electronic procurement system; external access blocked immediately
Authorities probe cause as utility moves to overhaul security systems and prevent secondary damage
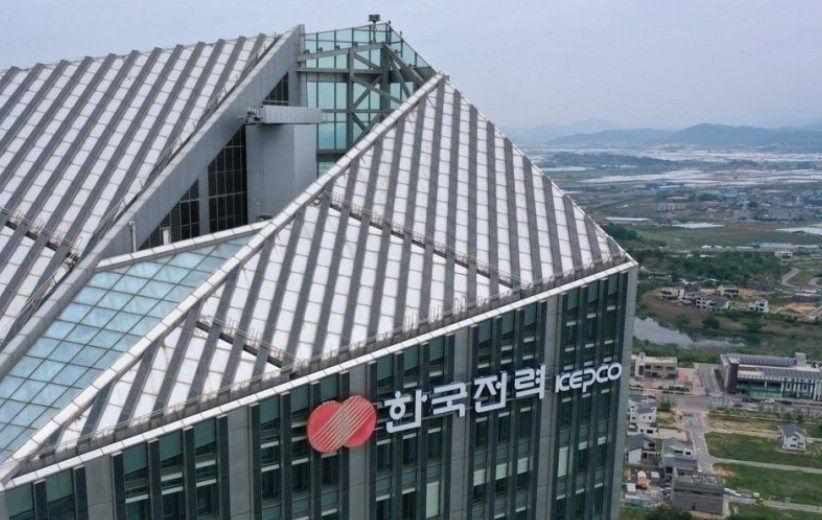
Korea Electric Power Corporation confirmed Sunday that personal data on about 1.5 million customers had been leaked — a second breach in as many months following an earlier incident involving employee records.
The utility said the breach affected 650,487 users of its customer service platform KepcoON and 870,000 users of its electronic procurement system, known as SRM, which handles purchasing, construction and service contracting.
For KepcoON users, 12 categories of data were exposed: customer numbers, names, resident registration and foreign registration numbers, phone numbers, addresses, bank names, account numbers, account holder names, card issuers, card numbers, card holder names and billing information. For the SRM, 426,827 corporate representatives had four data fields leaked — names, resident or foreign registration numbers, email addresses and company addresses — while 442,934 Korea Electric Power Corporation and corporate employees had six fields exposed, including names, affiliations, employee ID numbers, mobile phone numbers, email addresses and office phone numbers.
The utility said it became aware of the situation Friday and immediately cut off external IP access and suspended overseas services.
Korea Electric Power Corporation has begun notifying affected customers and launched a joint investigation with the National Intelligence Service, the Ministry of Climate, Environment and Energy's cybersecurity center and outside experts.
Last month, the utility disclosed a separate breach involving the names and phone numbers of 35,528 current employees, retirees and partner company staff, and said it had filed a request for a criminal investigation and taken follow-up measures.
Following the latest incident, Korea Electric Power Corporation immediately activated an emergency response center and began continuous monitoring to prevent secondary damage and guard against further cyber threats.
The utility has also set up a dedicated channel where customers can check whether their data was compromised and file damage reports, and said it has completed the mandatory notification under the Personal Information Protection Act.
Particularly concerned about customer anxiety over the exposure of financial data such as bank account and card numbers, the utility plans to share details with government and financial authorities and request enhanced monitoring for suspicious transactions to prevent secondary harm.
Korea Electric Power Corporation is working closely with the National Intelligence Service, the Ministry of Climate, Environment and Energy's cybersecurity center and outside experts to investigate the access routes and attack methods used, and to prepare for further AI-assisted cyberattacks. The utility said it is conducting a thorough review of its entire internet service infrastructure and plans to overhaul its security framework to defend against next-generation AI-based hacking.
"We take this incident very seriously and sincerely apologize for the concern caused to the public," Korea Electric Power Corporation President Kim Dong-cheol said. "We will thoroughly investigate the cause of the breach, fundamentally improve our information security systems, and do our utmost to protect personal data so that people can use our power services with confidence."
oskymoon@heraldcorp.com