Forum held with auditors from 21 major brokerages
'Fundamental reflection' needed on internal controls
Management urged to invest in audit capacity
The Financial Supervisory Service has sharply criticized the securities industry's internal controls, saying "chronic illegal practices that fail to meet even the most basic standards keep repeating themselves." The regulator pointed to ongoing cases in which brokerages include false or misleading information in product disclosures, or conduct investment solicitations over personal mobile phones to avoid leaving any record.
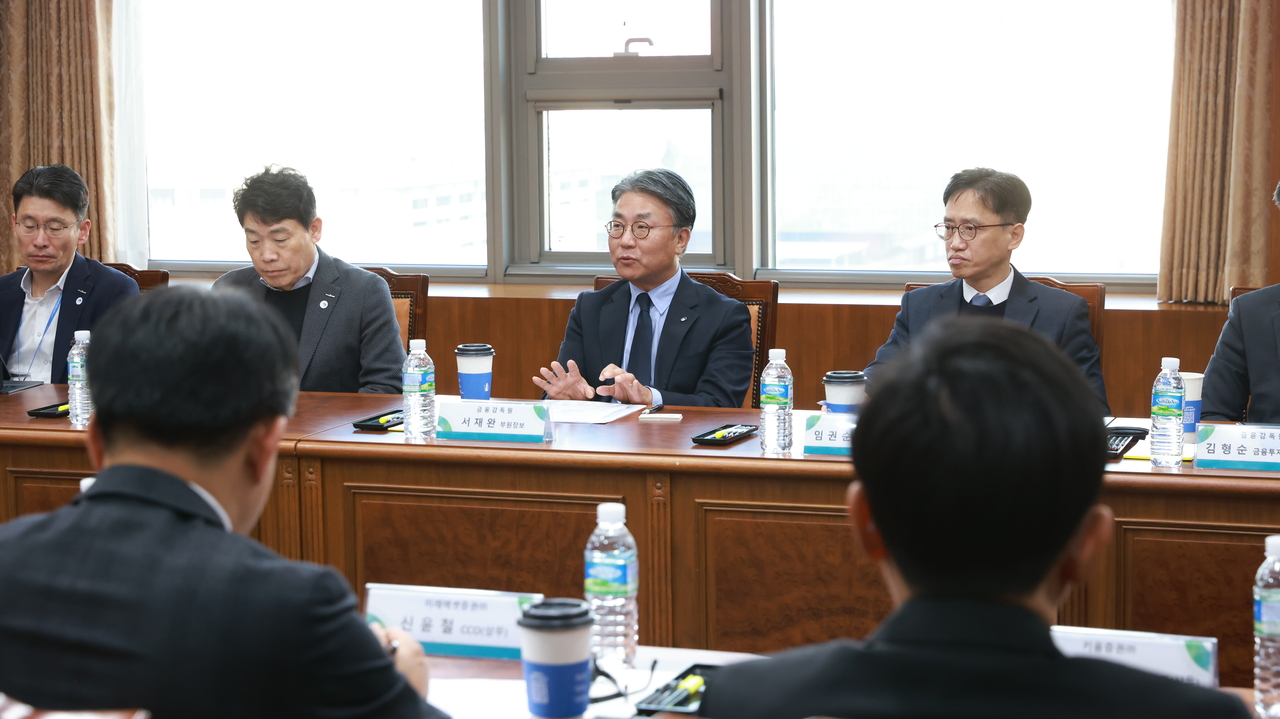
The FSS held a forum Wednesday at the Korea Financial Investment Association with auditors from 21 major securities firms to discuss ways to strengthen investor-centered internal audit functions. The regulator shared recent inspection findings and internal control advisories, and discussed measures to enhance investor protection through proactive auditing.
FSS Deputy Governor Seo Jae-wan, who delivered the opening remarks, said the industry's internal controls have failed to keep pace with its recent external growth.
"The record-level quantitative growth the securities industry has achieved in recent years rests on investors' expectations of fairness and transparency in the capital markets," Seo said. "Whether the current state of internal controls at securities firms is living up to those expectations and earning sufficient trust requires fundamental reflection and soul-searching."
He particularly took issue with the repeated failure to observe even basic rules at the front lines of customer-facing sales operations.
"Chronic illegal practices that fail to meet even the most basic standards keep repeating themselves — including recording false or inaccurate information in product disclosures provided to customers, and using personal mobile phones during sales activities so that no solicitation records are kept at all," Seo said. He added that he had "serious concerns that internal controls have not been functioning properly" while such conduct has continued.
Seo also warned that investor protection pledges issued by brokerages must not remain empty declarations. "The investor protection declarations and pledges that securities firms have made to their customers can no longer be mere stopgap slogans," he said, urging auditors to "rigorously examine, with an objective and neutral eye, whether investor protection processes are truly working as they should."
He also called for a shift away from the industry's practice of assigning blame only after an incident occurs. Seo said internal audit teams must "devote all efforts to proactive investor protection through preventive auditing, rather than after-the-fact auditing."
He directed the same message at management, telling executives not to treat internal audit units as mere cost centers. "CEOs and other executives need to stop viewing internal audits purely as a cost and instead actively build audit capacity through human and material support," Seo said.
The FSS said it will continue engaging with securities firms through consulting inspections and an internal audit consultation framework to ensure that voluntary internal audits and regulatory inspections work in tandem.
Seo also issued a warning over a string of recent personal data breaches in the financial sector, urging each securities firm to "conduct a full review of IT security and inspection systems with heightened vigilance" and to swiftly and accurately assess any potential investor harm, implementing protective measures immediately when necessary.
At the forum, the FSS also shared with securities firms the results of a recent review of product design and manufacturing processes, along with advisories on stock lending practices conducted in the course of liquidity provider operations.
The regulator also asked firms to ensure the smooth implementation of a voluntary margin financing management plan — under which firms are to keep their total credit exposure within 90 percent of equity capital, down from 100 percent, and voluntarily reduce margin financing in any single stock that exceeds 15 percent of the firm's total margin financing balance. Firms were also asked to self-assess their compliance with follow-up measures under a comprehensive advertising improvement plan aimed at eliminating false and exaggerated promotions.
Auditors from the participating securities firms agreed on the need to strengthen preventive auditing from an investor perspective. The firms said they would "go back to basics," reviewing whether investor protection and risk management systems across the entire sales process are functioning properly, and pledged to strengthen internal controls in cooperation with the regulator through consulting inspections.
The FSS said it will continue supporting financial investment firms in building proactive internal audit functions and audit capacity, while maintaining ongoing dialogue with the industry.
Meanwhile, financial authorities have identified 28 IP addresses linked to what are believed to be AI agent-assisted hacking attacks on the financial sector. The FSS said it had circulated 33 IP addresses — 28 after removing duplicates — associated with recent cyberattacks on financial institutions, along with information on some of the countries of origin.
th5@heraldcorp.com