Financial authorities probe cyberattacks at 7 banks and mutual finance firms
Regulators order fixes for authentication gaps, access control failures
Banks and card firms must complete checks by Tuesday; securities and insurers by Thursday
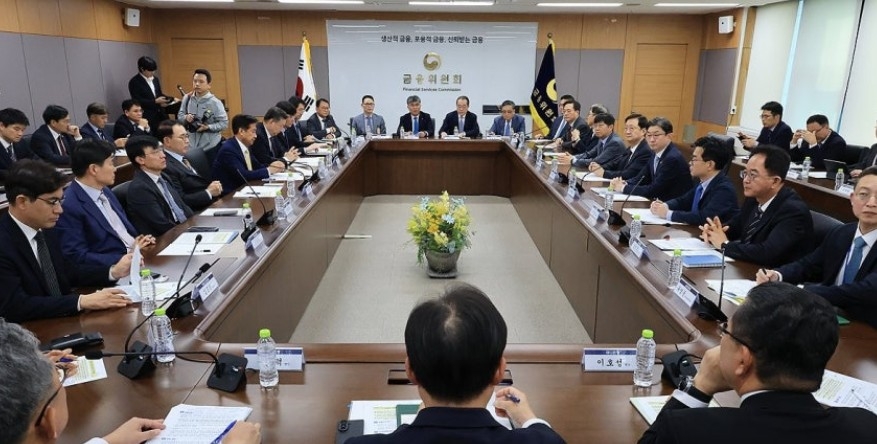
A wave of cyberattacks believed to involve AI tools has spread across South Korea's financial sector, with the same internet protocol addresses found at multiple institutions — raising the possibility that a single actor is behind the incidents.
The same attacker IP addresses were identified across breaches at seven firms: Shinhan Bank, KB Kookmin Bank, Hana Bank, BNK Busan Bank, Yegareum Savings Bank, Welcome Savings Bank and Hyundai Capital. The attacker is believed to have continuously cycled through different IP addresses to sustain the campaign.
Investigators believe the attacker used AI tools to carry out large-scale, automated attacks against multiple financial institutions simultaneously.
Documents Shinhan Bank submitted to the National Assembly show that the attacker used IP addresses from multiple countries, including South Korea, the United States, Japan, Hong Kong, Singapore, Vietnam, Thailand and the United Kingdom.
The breach at Shinhan Bank affected a supplementary system used by employees and loan solicitors. No customer-facing services — including internet and mobile banking — were disrupted, and no financial losses were reported.
Financial authorities have classified the hacking incidents into three categories and issued corresponding response measures.
In the case of information-inquiry services, investigators found that systems had been improperly developed to allow users to look up loan application records and corporate representative information without identity verification. Authorities ordered a full audit of all services with missing authentication steps, directing firms to either fix the errors or shut down the affected services.
For employee support services used by private bankers and relationship managers, authorities found that breaches occurred because mobile device access controls were absent or because unpatched web vulnerabilities allowed unauthorized access. Financial firms must tighten controls to permit access only from pre-registered devices and immediately address vulnerable web services.
In the case of website services, hackers exploited known security vulnerabilities to install malicious code and steal log files containing customer information. Authorities directed firms to patch the known vulnerabilities or block the affected services to strengthen security controls.
The Financial Supervisory Service has distributed the attacker IP addresses and security advisories to approximately 500 financial firms across the sector. Banks and card companies must complete emergency checks by Tuesday, while securities firms, insurers, savings banks and electronic financial service providers have until Thursday.
All firms must conduct their reviews using a 12-item checklist covering three areas: blocking attacker IP addresses and assessing the extent of any damage, identifying externally exposed IT assets and services, and verifying whether security has been strengthened. Any deficiencies found must be remedied immediately.
Financial authorities plan to conduct on-site inspections at affected companies and share findings on vulnerabilities and remediation cases with the broader financial sector to prevent similar incidents from recurring.
ko@heraldcorp.com