No signs of external cyberattack
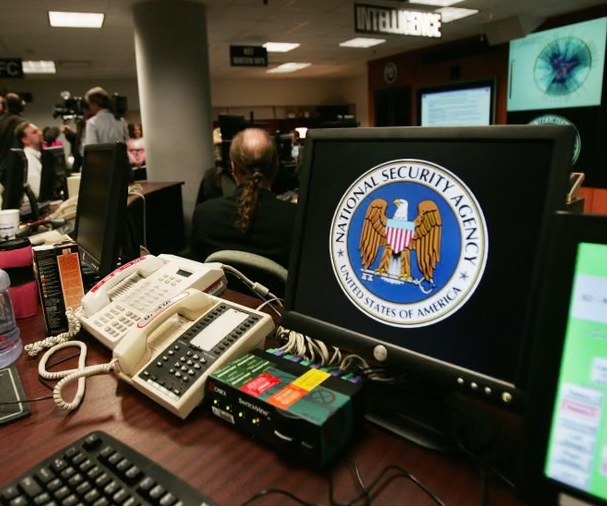
The National Security Agency's core internal communications network suffered an outage lasting more than three days, disrupting work for employees across the agency. The problem is believed to have stemmed from a software update rather than an external cyberattack.
According to CNN, the outage affecting NSANet — the NSA's internal network — was resolved Friday (local time).
Sources familiar with the matter and a voicemail recording left for employees at NSA headquarters in Maryland said the agency, immediately after restoring the network, directed staff to stagger their login times to prevent the system from being overwhelmed by simultaneous connections.
NSANet serves in effect as the NSA's classified internal email system. The outage prevented employees from accessing the network, causing significant disruption to day-to-day operations.
One source said there were multiple instances of employees coming in under the staggered schedule only to find they could not log into the system at all and had to return home.
The NSA is an intelligence agency under the US Department of Defense responsible for foreign signals intelligence collection and analysis, cryptanalysis, and cybersecurity.
A senior US administration official said the software patching required to resolve the outage took longer than expected. Current and former officials said NSANet has experienced outages before, but that one lasting this long and causing this level of operational disruption was unusual.
However, the NSA's core intelligence-collection functions remained intact throughout the outage. Multiple officials said the most sensitive collection systems continued normal operation during the disruption, and that backup systems and workarounds were in place to substitute for the classified email network.
The outage was not the result of an external cyberattack, officials said.
Multiple current US officials said the problem may have arisen during a software update intended to address a security vulnerability in PHP, a programming language widely used across websites around the world.
The vulnerability was reportedly discovered and disclosed last month by private security researchers using AI tools. The NSA had earlier advised agencies to apply the relevant software security patch.
quq@heraldcorp.com