North Korean hackers breach world's largest crypto exchange
Single heist nets 8 trillion won — 'largest ever' virtual asset theft
Six or more groups, including Lazarus and BlueNoroff, operate globally
Theft scale growing tenfold each year as Pyongyang funds nuclear program
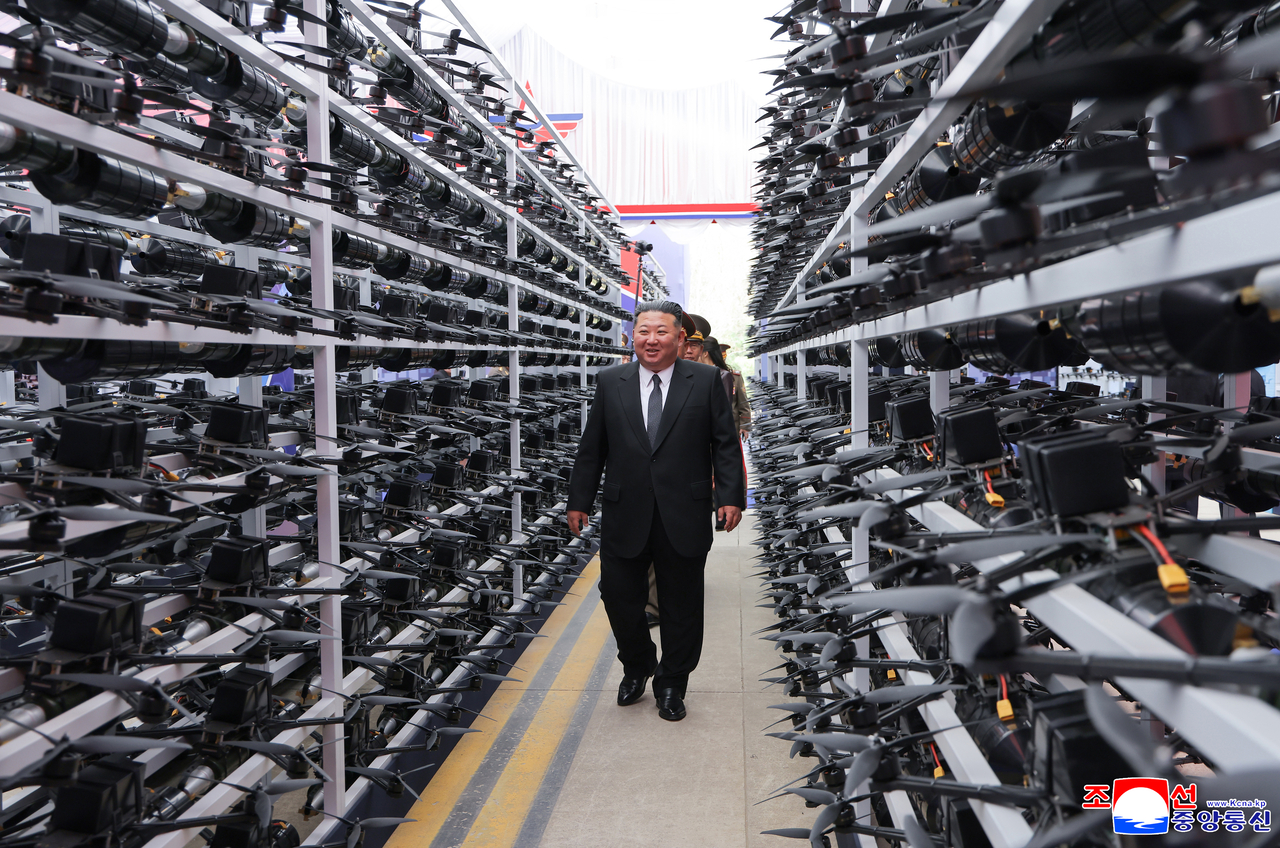
Binance, the world's largest cryptocurrency exchange, suffered a hack of approximately $6.3 billion on Oct. 29 (local time).
US blockchain intelligence firm TRM Labs identified North Korea as the perpetrator and called the incident "the largest virtual asset theft in history." TRM Labs named North Korean hacking group TraderTraitor as the central actor behind the attack.
TraderTraitor is a North Korean hacking group that the US Federal Bureau of Investigation and the Cybersecurity and Infrastructure Security Agency identified in 2022 as a threat targeting global virtual assets and related platforms.
Living up to US intelligence concerns, TraderTraitor carried out a string of major heists: in June 2023, it hacked cryptocurrency wallet platform Atomic Wallet for $100 million; in July of the same year, it struck virtual asset payment platform Alphapo for $60 million and Estonian cryptocurrency firm CoinsPaid for $37 million.
In May 2024, the group extracted $308 million from Japanese cryptocurrency exchange DMM Bitcoin. In February last year, it stole approximately $1.5 billion in virtual assets from Bybit, a global crypto exchange based in Dubai, UAE. This year, it pulled roughly 8 trillion won from Binance.
If 2023 saw thefts in the tens of billions of won range, 2024 brought hundreds of billions, and 2025 has reached the trillions — a tenfold-plus expansion in cyber-plundering capacity each year. At this pace, analysts say thefts in the tens of trillions of won are conceivable next year, and hundreds of trillions the year after.
From tens of billions in 2023 to hundreds of billions in 2024 to trillions in 2025
The hackers are known to employ social engineering techniques that exploit the trust of insiders at targeted organizations. Once a victim is tricked into running malicious software, the attackers gain access to the device and use it as a foothold to penetrate internal systems and launch a full-scale breach.
The name TraderTraitor derives from the group's signature method of turning traders into unwitting traitors. As the name suggests, TraderTraitor is less a standalone hacking organization than a label for a particular attack methodology.
The group is believed to be linked to Lazarus, North Korea's most widely known hacking organization. North Korea is assessed to operate at least six hacking groups on the global stage, Lazarus among them.
In February 2023, the South Korean government designated four individuals and seven institutions as sanctions targets for financing North Korea's nuclear and missile programs through cyber operations — the first independent cyber-specific sanctions Seoul had ever imposed against Pyongyang.
The four sanctioned individuals were Park Jin-hyeok, Cho Myong-rae, Song Rim and O Chung-song. The seven sanctioned institutions were Lazarus, BlueNoroff, Andariel, Chosun Expo Joint Venture, the Technical Reconnaissance Bureau, Lab 110 and the Automation University (Mirim College).
Of the seven institutions, Mirim College is a hacker-training academy; the remaining six are all hacking organizations under North Korea's Korean People's Army Reconnaissance General Bureau.
The Reconnaissance General Bureau was established in February 2009 through the merger of the KPA General Staff's Reconnaissance Bureau, the Korean Workers' Party's Operations Department and its External Intelligence Investigation Department (Office 35) — all previously separate intelligence and covert-operations bodies. Notably, North Korea's cyber offensive activities accelerated sharply from the same year the bureau was founded.
The organization is broadly comparable to the US Defense Intelligence Agency or Russia's Main Intelligence Directorate. It is also seen as analogous to South Korea's Defense Intelligence Agency, which oversees units such as the Korea Defense Intelligence Command and the 777 Command. In September last year, North Korea reorganized and expanded the Reconnaissance General Bureau into the Reconnaissance General Information Bureau.
The Reconnaissance General Information Bureau comprises six operational departments: Bureau 1 (Operations), Bureau 2 (Reconnaissance), Bureau 3 (Foreign Intelligence), Bureau 5 (Inter-Korean Coordination), Bureau 6 (Technology) and Bureau 7 (Rear Support).
Bureau 3, which handles cyberattacks, is also known as Bureau 121 — the Cyber Warfare Guidance Bureau. Its headquarters is believed to be located in the Musindong area along the Taedong River in Pyongyang.
Lab 110 (the Computer Technology Research Center), a subordinate unit of Bureau 3 — Bureau 121 — is known as the base of operations for Lazarus, BlueNoroff, Andariel and Kimsuky (also known as Thallium). These groups largely overlap with the targets of South Korea's first independent cyber sanctions against the North.
The former Reconnaissance General Bureau was known to carry out special operations including agent training and infiltration, intelligence collection, assassination of key figures and abductions. In its predecessor form, it was behind the 1968 armed infiltration in Uljin and Samcheok and the 1996 armed infiltration in Gangneung.
The sinking of the corvette Cheonan in March 2010, the shelling of Yeonpyeong Island in November 2010, the planting of land mines in the DMZ in 2015 and the assassination of Kim Jong-nam in 2017 have all been attributed to the bureau.
North Korean troops deployed to the war in Ukraine in October 2024 also fall under the Reconnaissance General Bureau's command.
North Korea's cyber offensive intensifies after 2009 Reconnaissance General Bureau overhaul
North Korea's first known cyberattack came on July 7, 2009, when distributed denial-of-service strikes hit 35 major government and institutional websites in South Korea and the United States. Four subsequent waves of attacks disrupted 68 key websites, including those of government agencies.
Those DDoS attacks expanded in scope with an assault on agricultural cooperative bank NongHyup's financial computing system in April 2011, and in March 2013 domestic broadcasters including KBS and MBC were added to the target list.
In December 2014, North Korea hacked Korea Hydro & Nuclear Power at home before breaching Sony Pictures in the United States — a move that thrust Pyongyang onto the global stage and drew worldwide attention. Sony Pictures was preparing to release "The Interview," a film depicting the assassination of Kim Jong-un. The studio reportedly suffered losses of around 100 billion won from the hack.
In October 2015, hackers targeted the Seoul subway system and attempted to breach Cheong Wa Dae and foreign and security ministries.
North Korea's fourth nuclear test on Jan. 6, 2016, marked a turning point that fundamentally transformed the nature of its cyber operations.
From that point on, the strategic objectives of global cyberattacks led by the Reconnaissance General Bureau shifted decisively toward overcoming the foreign currency shortages caused by international sanctions and securing funds for nuclear and missile development.
Following the fourth nuclear test, North Korea conducted a total of three nuclear tests (the fourth, fifth and sixth) and 44 ballistic missile test launches before declaring the completion of its national nuclear force in November 2017 after successfully testing the Hwaseong-15 intercontinental ballistic missile — a trajectory that left it no choice but to face sweeping international sanctions.
The UN Security Council passed 10 resolutions aimed at halting North Korea's nuclear and missile programs.
Sanctions after 2016 nuclear test shift North Korea's hacking goals toward cash
In response, North Korea orchestrated a hack against Bangladesh's central bank in 2016, stealing $81 million. In February 2017, it breached domestic cryptocurrency exchange Bithumb and made off with $7 million.
Four additional attacks on Bithumb followed, bringing total losses from the exchange to an estimated $65 million. Emboldened by those successes, the group accelerated its push overseas.
In May 2017, North Korea launched ransomware attacks against financial institutions in more than 150 countries, an incident that led the international community to recognize Pyongyang's cyber threat as a serious national security crisis.
In November 2019, it attacked domestic cryptocurrency exchange Upbit, causing losses of 56 billion won. In September 2020, it hacked a Slovak cryptocurrency exchange and netted approximately $5.4 million.
In the first half of 2021, the group attacked Korea Aerospace Industries and the Korea Atomic Energy Research Institute. That April, it also deployed ransomware against hospitals in Kansas and Florida, extracting $500,000.
In March 2022, it hacked the blockchain-based game Axie Infinity for $615 million — what was at the time the largest crypto heist on record.
The FBI attributed these attacks to North Korean hacking group Lazarus, which had previously been identified as the perpetrator behind the 2014 Sony Pictures hack and the 2017 ransomware attacks.
Lazarus, Hidden Cobra, Guardians of Peace — similar but distinct
Lazarus goes by many aliases — TraderTraitor, APT38, BlueNoroff, Hidden Cobra and Guardians of Peace among them — a reflection of the fact that its true structure remains only partially understood.
The group is believed to have been established under the Reconnaissance General Bureau in 2007, with different names assigned depending on the methods, targets and objectives of each operation.
The origin of the name "Lazarus" is itself a matter of debate.
Lazarus is the English name for the biblical figure who is said to have risen from the dead four days after his burial — a symbol of resurrection and revival. The name is sometimes interpreted as a reference to a group that persists relentlessly despite tracking and sanctions.
The name was, however, simply coined by a foreign cybersecurity firm for convenience while tracing North Korean hacking activity.
Competing theories abound: one holds that the name originated in a 2016 report titled "Operation Blockbuster," published by security firm Novetta while investigating the 2014 Sony Pictures hack; another suggests it was taken from the username of the Sony Pictures hacker; a third claims it was borrowed from a character in the game Diablo.
BlueNoroff and Andariel are classified as subgroups of Lazarus.
Both are primarily associated with attacks on financial institutions and cryptocurrency-related targets. BlueNoroff in particular is identified as the main perpetrator of the 2016 Bangladesh central bank hack.
Russian cybersecurity firm Kaspersky coined the name BlueNoroff after analyzing the group's attacks on financial institutions and concluding it was a separate organization from Lazarus — naming it after a hacking tool the group had used.
Andariel shares its name with one of the seven prime evils in Diablo. Active since 2008, it has focused primarily on defense-sector targets including arms manufacturers, shipbuilders and other defense industry entities.
The division of labor appears deliberate: Lazarus handles financial targets, Andariel focuses on the defense industry, and Kimsuky concentrates on government agencies — evidence of close, structured coordination.
Kimsuky, active since 2010, got its name after Russian security firm Kaspersky published a report on North Korean hacker Kim Suk-yang using an email account linked to that name. The firm dropped "ang" from "Kimsukyang" and published the shortened form "Kimsuky."
Kimsuky is known to spread malware through phishing emails and conduct information theft operations. It has carried out intensive intelligence-gathering campaigns against South Korean, US and Japanese government agencies and foreign and security policy think tanks, and is believed to be the same organization as the hacking group known as Thallium.
North Korean authorities are expected to continue expanding the hacking organizations under the Reconnaissance General Bureau's umbrella. To that end, a program to identify the country's top talent and train them as hackers is reported to be in full operation.
Kim Jong-un has emphasized cyber capabilities alongside nuclear and missile forces as the regime's "two great swords" since early in his rule. In July, Kim announced plans to further expand the roles and missions of the Reconnaissance General Information Bureau.
North Korea's cyber warfare personnel are currently estimated at a minimum of around 8,400.
South Korea's Defense Ministry put the figure at around 6,800 in its defense white papers from 2016 through 2022, but the National Intelligence Service and other intelligence agencies revised the estimate upward to around 8,400 as of 2024.
soohan@heraldcorp.com