
Data of 5,600 of 6,444 affected customers protected by encryption
Resident registration numbers, ID copies among leaked information; exchange's core network said to be safe
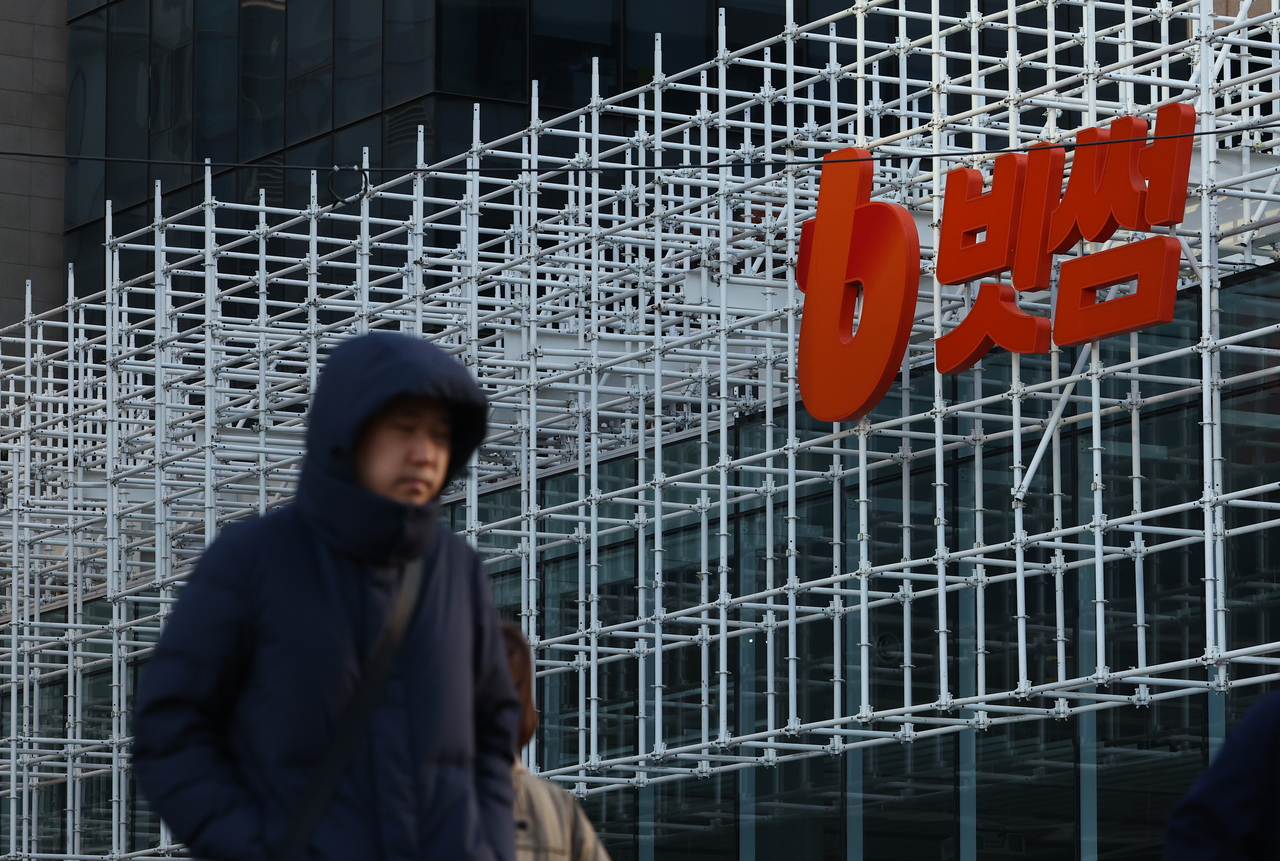
A hack of digital asset exchange Bithumb's internal mobile system has resulted in the leak of personal data belonging to 844 customers and 715 employees, the company confirmed.
According to industry sources, an unauthorized external party gained access Tuesday to Daou Office, Bithumb's internal mobile groupware system. Bithumb reported the incident to the Korea Internet & Security Agency at 11:39 p.m. that day and to the Personal Information Protection Commission at 12:48 a.m. Wednesday.
Bithumb said a total of 6,444 customers were associated with the breach. Of those, the data of 5,600 were stored in encrypted files and remained inaccessible to outsiders, leaving 844 customers whose personal information was actually exposed.
The leaked data included, beyond names, mobile phone numbers, email addresses, resident registration numbers, driver's license numbers, bank account numbers and copies of identification documents. The scope of information leaked varies by customer, Bithumb said. Personal data of 715 employees was also compromised.
The breach is believed to have exploited a vulnerability in the internal mobile groupware system provided by a third-party vendor. Customer personal data was exposed in the course of employees using the groupware for work purposes.
The intrusion occurred between 11:28 a.m. and 12:27 p.m. Tuesday. Bithumb said it first detected the abnormal access at 12:14 p.m. that day, promptly blocked the attacker's access route and suspended all use of the mobile groupware. The company is currently conducting security checks and applying patches in cooperation with the service developer.
Bithumb said the groupware system affected in the breach is an internal work platform separate from exchange accounts and customer asset data. The company said there is no indication that the exchange's services or customer databases were directly compromised.
Starting Thursday afternoon, Bithumb said it would notify affected customers individually in stages. Customers can also check whether their information was leaked through the company's website.
In addition, Bithumb urged customers to be wary of anyone impersonating company employees to request authentication codes or prompt app installations. The company directed customers to report related incidents or submit inquiries through its official customer service center.
"I sincerely apologize for the concern and anxiety this has caused our customers," Bithumb Chief Executive Lee Jae-won said. "If secondary damages are confirmed for customers whose personal information was leaked, we will do our utmost to provide relief and compensation."
"We will take this incident as an opportunity to review our entire internal infrastructure security framework from the ground up and devote all efforts to preventing a recurrence," Lee added.
Meanwhile, the National Security Office at Cheong Wa Dae convened an emergency meeting Wednesday afternoon to address a series of simultaneous hacking incidents in the financial investment sector. The session, titled "Emergency Review Meeting on Serial Hacking in the Financial Sector," was chaired by Third Deputy Director Song Ki-ho.
kyoung@heraldcorp.com




