Lawmaker Kim Yong-man criticizes regulators for holding meetings instead of preventing breaches; FSS chief pledges near-comprehensive inspection
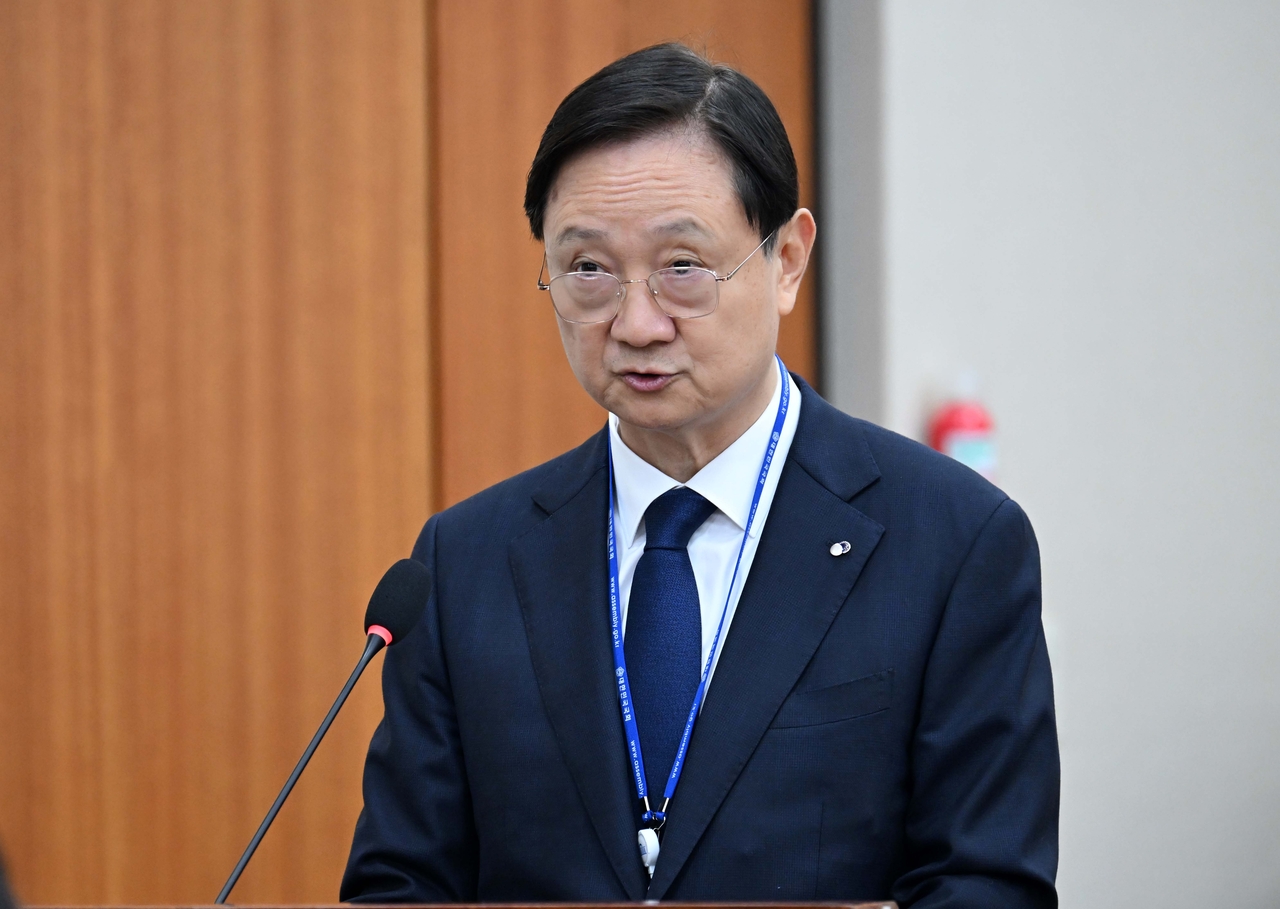
Financial Supervisory Service Governor Lee Chan-jin said Monday that recent hacking and personal data breach incidents in the financial sector could become the first case in which a CEO is held accountable for failing to fulfill internal control management obligations.
Lee made the remarks at the FSS national audit by the National Assembly's Political Affairs Committee, responding to questions from Democratic Party of Korea lawmaker Kim Yong-man. "This will be the first case in which a CEO's obligation to manage internal control standards is addressed in connection with a cybersecurity hacking incident," Lee said.
Kim said financial authorities had focused on holding meetings rather than taking substantive action, and had failed to prevent the breaches as a result. "Just two weeks before the incident, the Korea Financial Security Institute called in security officers from each bank for a seminar on AI security threats in finance, and in June there was also a meeting to strengthen financial firms' incident-response capabilities," Kim said. "And yet this kind of incident still happens."
Kim said security vulnerabilities were recurring not only at major banks but also across second-tier financial institutions. "An Oct. 8 review of 12 items found that more than 130 out of 555 institutions had inadequate security," he said, calling for the FSS to conduct a full inspection directly.
Lee acknowledged there were "practical limitations" to a full-scale inspection, but said the FSS had already conducted comprehensive checks on the most vulnerable areas and was now moving to sampling-based reviews. "We will carry out the inspection to the greatest extent possible, at a level equivalent to a full inspection," he said.
Kim also raised concerns about the delayed timeline for easing network-separation regulations, which had been pushed back from the originally scheduled date of Oct. 7 amid the string of financial sector incidents. "Don't you think deregulation of network separation is necessary to counter AI-based hacking with AI?" he asked.
Lee said a full-scale easing of network-separation rules was difficult at this stage. "There seems to be a need to stay true to the basics while transitioning step by step to an AI-based security framework," he said. He added that the FSS's fundamental approach was to first verify that institutions were minimizing external exposure and adhering to basic security principles.
won@heraldcorp.com