ARTEX Pro launches after open-source version goes dark
Security foundations remain weak as AI hacking tools advance
Tensions are rising again in South Korea's banking sector as ARTEX, an AI-powered penetration testing tool linked to a series of cyberattacks on domestic financial institutions, has resurfaced in a commercial version. The reappearance comes amid persistent gaps in cybersecurity staffing, external system management and vendor oversight — and as AI-driven attack methods continue to evolve rapidly. While attackers this time exploited so-called "side doors" in peripheral support systems, security experts warn that core financial networks could be the next target.
Chinese cybersecurity firm ThreatBook on Saturday unveiled a cloud-based AI penetration testing platform called RedAgents.AI. The platform hosts several AI penetration testing agents, including ARTEX Pro — the commercial successor to ARTEX — alongside YanJi, YanXun and CyberStrikeAI. ARTEX had been pulled from public access after evidence emerged that its open-source version was exploited in attacks targeting South Korean financial institutions from late last month through earlier this month. It returned as a commercial service within days.
ARTEX uses large language models to automate vulnerability scanning, attack path mapping and security tool execution. Its ability to rapidly and repeatedly probe for weaknesses that would otherwise require manual discovery makes it a potent threat — capable of identifying gaps across multiple systems in a short time if weaponized.
The recent wave of attacks on the financial sector illustrates exactly that risk. Rather than targeting core transaction systems head-on, the attackers zeroed in on vulnerabilities in peripheral systems — including platforms used by loan solicitors and employee support tools — that had received comparatively little security attention. The breach was less a matter of breaking through a strong defense than of quickly locating long-neglected back doors using AI tools.
"Shutting down ARTEX alone does not solve the problem," said Kwon Tae-kyung, a professor at Yonsei University's Graduate School of Information. "There are already many similar tools out there, and many people have downloaded the open-source version of ARTEX, so variants will keep appearing. If autonomous penetration tools become coupled with more advanced LLMs, we could see incidents far more serious than what we have now."
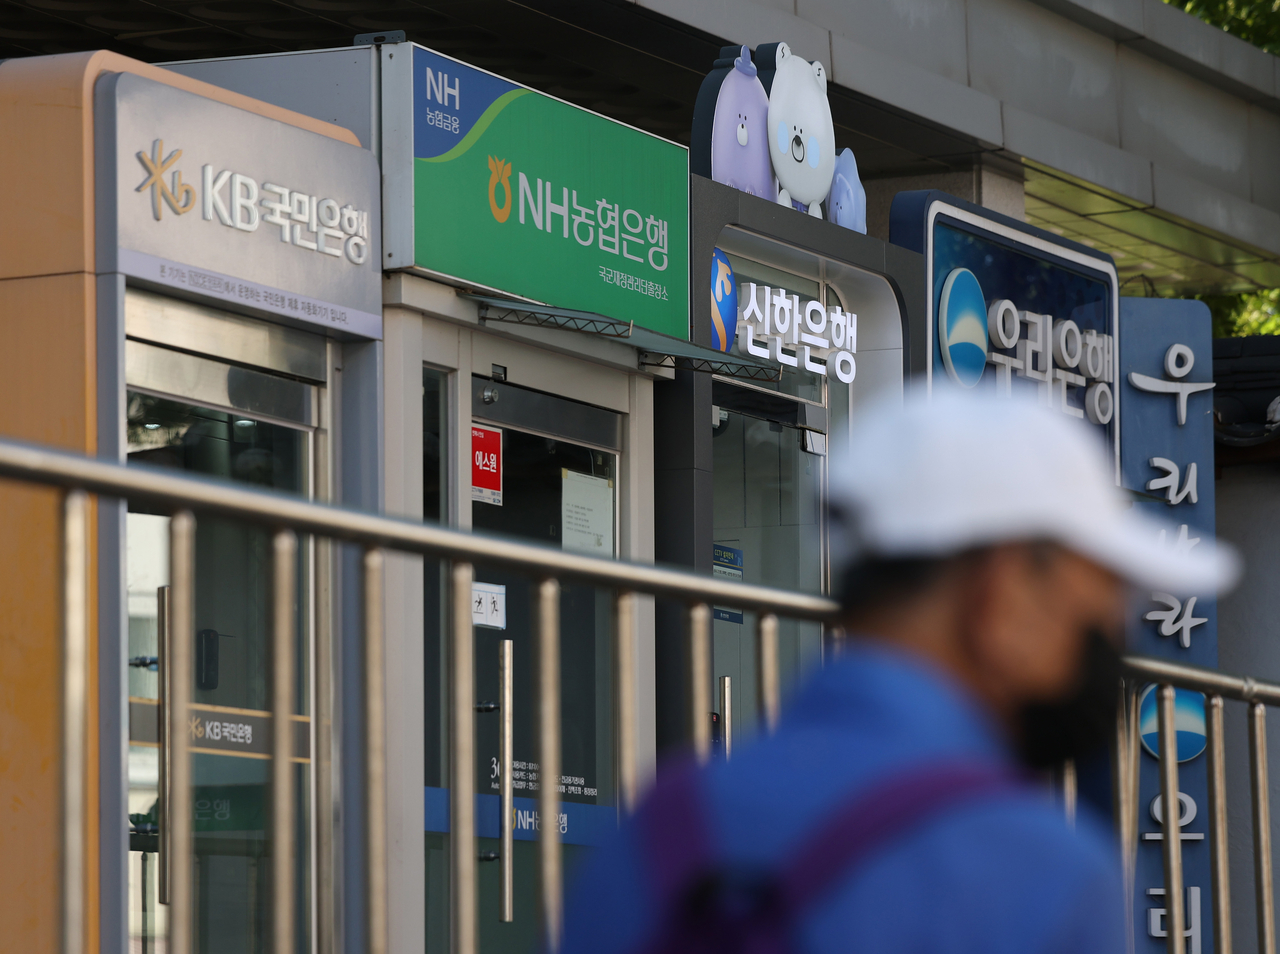
While attacks on the financial sector continued over the same period, the extent of damage varied by institution. Customer data breaches were confirmed at Shinhan Bank, KB Kookmin Bank and Hana Bank, while Woori Bank and NH NongHyup Bank reported no confirmed data leaks from the same attacks. Industry observers cite differences in basic security practices — including whether multi-factor authentication and access controls were in place, and the scope of externally exposed support systems — as among the factors that determined which institutions were affected. Financial regulators have so far identified 16 financial companies, including banks, as victims of the intrusions, with roughly 100,000 records compromised.
The deeper question is whether the professional workforce needed to defend against and supervise threats is keeping pace with the speed at which attack tools are advancing. Data submitted to the National Assembly's Political Affairs Committee by the Financial Supervisory Service, obtained by People Power Party lawmaker Seo Il-jun, showed that as of late September, just 49 of the FSS's 2,236 staff — or 2.2 percent — held information security certifications. Of those, 31 held the Certified Information Systems Auditor designation, 11 held the Certified Information Systems Security Professional credential, and one held a domestic information security engineer certificate.
The five major banks fared no better, with certified information security professionals accounting for less than 1 percent of total staff at each institution. The share of certified employees ranged from 0.28 to 0.52 percent across the banks, and across all five combined, just 285 of 68,565 employees — 0.42 percent — held relevant certifications. Even within IT departments, the certification rate ranged from only 4.55 to 7.14 percent. While certifications do not fully capture an organization's actual capacity to respond to cyberattacks, they serve as one indicator of baseline expertise — and the figures have prompted concern that the sector needs to broaden its pool of specialists as AI-powered attacks grow more sophisticated.
Security experts warn that the scope of attacks could expand beyond peripheral support systems to strike at the heart of core financial infrastructure. Advanced LLM-based attacks could evolve to identify zero-day vulnerabilities, penetrate networks and then move laterally within internal systems to widen their reach.
Financial regulators have begun broadening their oversight. A review of 555 financial companies conducted through Wednesday found deficiencies at 130 of them, including failure to apply security patches, poor management of aging systems and the absence of round-the-clock monitoring. Inspectors also found cases where authentication and authorization controls were missing from external systems, and where multi-factor authentication had not been implemented for critical services. Authorities plan to conduct a sector-wide security review and increase vulnerability assessments at large financial firms to at least twice a year.
Some experts are calling for more fundamental action. "Patching problems one by one after each incident risks creating even bigger problems down the line," Kwon said. "We need to establish a task force involving the government, the financial sector and specialists, and set decade-long goals to build cybersecurity capacity over the long term."
rim@heraldcorp.com
hyuk@heraldcorp.com