Second breach hits same program five months after first
20,028 users' data leaked through AI solution provider
SQL injection attack on admin page confirmed
Breach made public 60 hours after it occurred
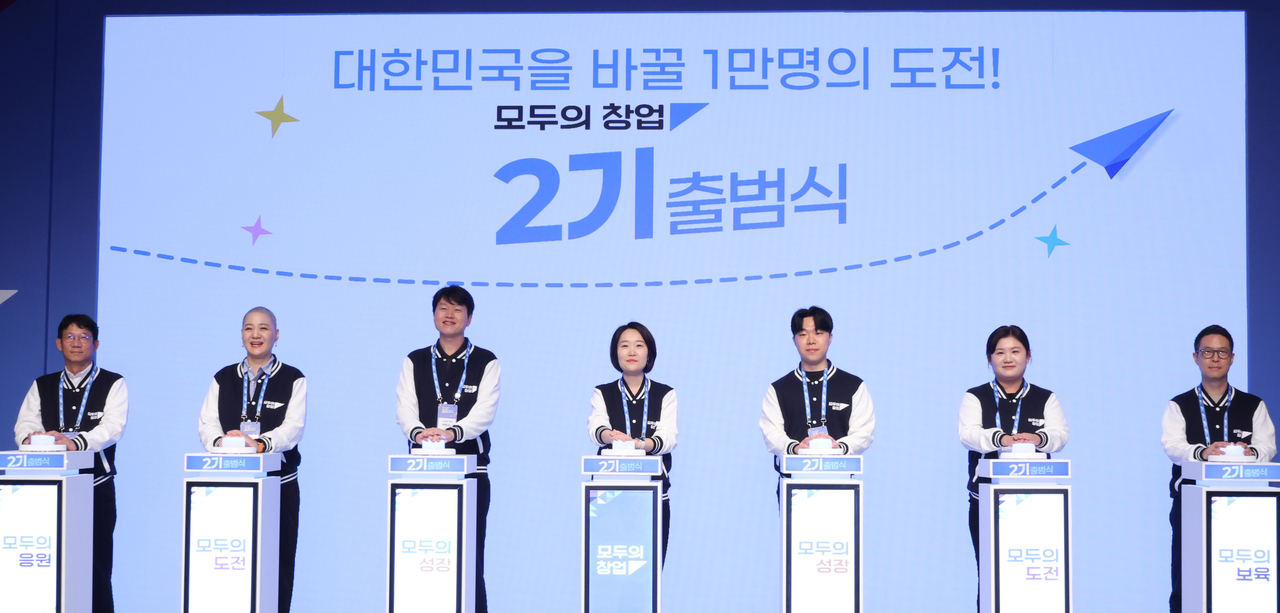
A personal data breach has struck the government's startup support program Modu-ui Changup for the second time. Despite the Ministry of SMEs and Startups pledging to strengthen application programming interface (API) security after the first incident in June, API-related vulnerabilities have surfaced again. The breach occurred at a private company that had passed the government's own security evaluation, raising questions about gaps in the ministry's oversight of partner firms.
According to the IT industry and the Korea Internet & Security Agency (KISA), an external hacking attack hit Amicus Rex — an AI solution provider participating in the second phase of the Modu-ui Changup program run by the Ministry of SMEs and Startups — on Wednesday.
The attack exposed the personal data of 20,028 users held by the company, including 818 participants in the Modu-ui Changup project. The leaked information included names, phone numbers and email addresses.
Amicus Rex operates Lawform, an AI solution that helps businesses draft legal documents. The Ministry of SMEs and Startups selects private AI solution providers and subsidizes usage fees so that program participants can access AI services during the startup preparation process.
The central concern is the security vulnerability exposed during the hack.
In the breach report Amicus Rex submitted to KISA and other authorities, the company said it had "confirmed an attempt to steal some information via an SQL injection attack on the administrator page" and had deleted vulnerable API code as a remedial measure.
An SQL injection attack involves entering malicious commands into a website or application to gain unauthorized access to a database. Attackers can exploit weak input-handling functions to retrieve or extract stored data.
After confirming signs of the attack, the company deleted the vulnerable API code. The incident again points to security weaknesses in the system handling external requests.
The first phase of Modu-ui Changup also suffered a personal data breach through an API vulnerability.
In that case, investigators found that some APIs on the program's official platform could be called externally and that information could be collected through web crawling.
That breach exposed the email addresses, evaluation comments and startup idea summaries of 5,000 first-round applicants. Encrypted data and the decryption keys needed to unlock it were also found to have been exposed.
In late July, the Ministry of SMEs and Startups announced preventive measures, pledging to strengthen personal data encryption, improve API access logging and enhance anti-crawling functions.
About five months later, however, a data breach at a partner company in the same program has reignited questions about the effectiveness of those measures.
The two incidents differ in their attack methods and the systems affected. The first breach involved non-public information on the government's official platform being exposed to external requests, while this time an SQL injection attack was confirmed on a system operated independently by a private company.
Critics say the government should have gone beyond securing its own official platform and verified the data protection standards of participating companies as well.
The company where the breach occurred had cleared the ministry's pre-screening process.
On Oct. 12, the Ministry of SMEs and Startups announced it had selected 50 AI solution providers and 103 AI solutions through a review panel of AI and software experts.
The ministry said the panel had evaluated the services firsthand, assessing not only technical quality and pricing but also security standards.
Yet a data breach at one of the selected companies within a month of the results being announced has prompted questions about whether the security evaluation was thorough enough to catch actual vulnerabilities.
The time it took to disclose the breach has also drawn criticism.
According to Amicus Rex's report, the hack occurred at 5:38 a.m. Wednesday. The company said it became aware of the incident at 8:30 a.m. the same day and reported it to KISA at 3:45 p.m.
The Ministry of SMEs and Startups, however, did not make the breach public until 5:08 p.m. Friday.
That amounts to roughly 59 hours and 30 minutes from the time of the hack to public disclosure, and about 49 hours and 23 minutes after the KISA report was filed.
The ministry said it was notified of the breach late. The Ministry of SMEs and Startups and the Korea Startup Promotion Agency said they were informed of the leak by the company at 6:10 p.m. Thursday.
Following the attack, the company blocked access from overseas IP addresses and took other security measures. On Friday afternoon, it individually notified the affected users whose data had been confirmed as leaked.
The Ministry of SMEs and Startups and the Korea Startup Promotion Agency also informed affected participants of the details of the incident and the type of data exposed, urging them to guard against follow-on harms such as smishing — fraud carried out via text message.
The ministry emphasized that the breach did not occur on a government-operated platform.
"The system where this breach occurred is operated independently by a private company and is separate from the program's official platform," a ministry official said. "The ministry and the Korea Startup Promotion Agency were notified of the personal data breach by the company at 6:10 p.m. Thursday, and we are working to prevent further damage and taking necessary steps, including investigating the circumstances of the incident."
The government has also asked other AI solution providers participating in the program to review the security of their own systems and their personal data management practices. It plans to continue checking data access controls and whether data past its retention period has been properly destroyed.
kwater@heraldcorp.com