Abnormal access detected and blocked immediately; CEO pledges customer protection and prevention measures
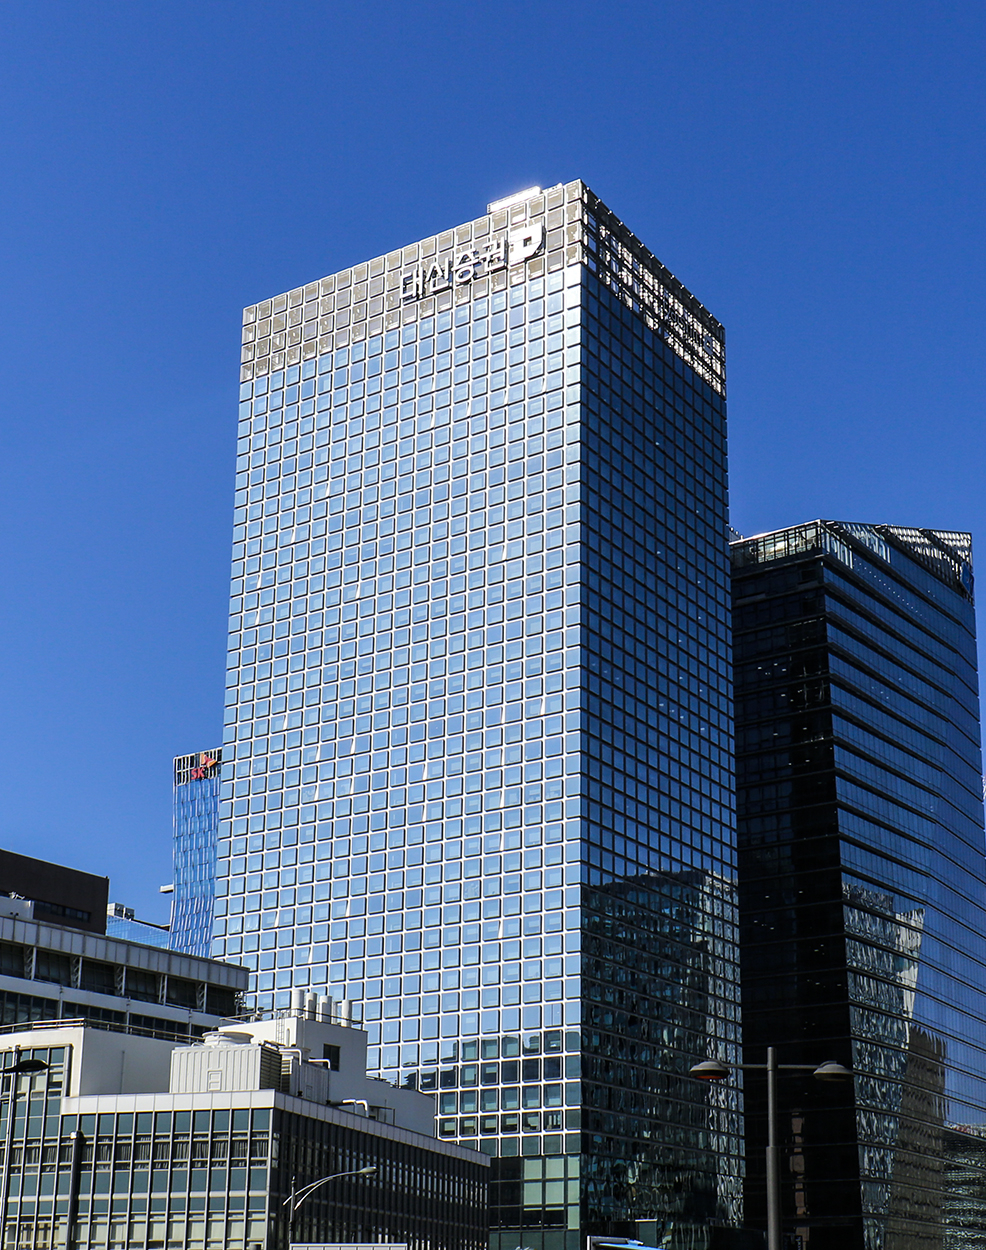
Daishin Securities has apologized for a leak of customers' personal and credit information and announced steps to prevent a recurrence, as a wave of hacking incidents that swept through banks and other financial institutions appears to be spreading to the securities industry.
The brokerage said Wednesday that an internal investigation had confirmed the personal data of 38,490 customers had been compromised, and that it was putting in place customer protection and recurrence-prevention measures for those affected.
The breach came to light on Oct. 17, when signs of unauthorized access by a hacker were detected on a server linked to the non-face-to-face account-opening service for discretionary investment accounts. Immediately after detecting the abnormal external access, the company blocked the IP addresses used in the attack and those used for bypass connections, and launched emergency response measures.
At the same time, Daishin Securities reported the incident to regulators and conducted a detailed forensic investigation with the Korea Financial Security Institute to determine the scope of the intrusion and whether personal and credit information had been exposed.
After a 10-day review of more than 60,000 signals disguised as normal service traffic, the company confirmed Monday that eight categories of data had been leaked: customer names, email addresses, physical addresses, telecommunications IDs, bank names, deposit and withdrawal account numbers (encrypted), Daishin Securities comprehensive account numbers (encrypted), and mobile phone numbers (encrypted).
However, no evidence of secondary damage to customers resulting from the breach has been found so far. Hackers did not gain unauthorized access to core business systems.
Daishin Securities said it would individually notify affected customers of the specific items exposed and take prompt action if any harm is confirmed. To prevent a recurrence, the company plans to strengthen access controls and anomaly-detection and blocking systems on the affected server, and to step up security-vulnerability checks on externally linked systems. Customers who suffer losses as a result of the personal and credit information leak will be compensated in accordance with applicable laws and procedures.
"We take this leak of personal and credit information extremely seriously and offer our deepest apologies to our customers," Daishin Securities Chief Executive Jin Seung-wook said. "We will responsibly carry out all measures necessary to protect customers and prevent a recurrence."
Financial Supervisory Service Governor Lee Chan-jin also addressed the incident at a breakfast meeting with bank holding company board chairs held at the FSS headquarters in Yeouido, Seoul, on Wednesday. "I understand that a broad hacking incident occurred at major financial investment firms on Tuesday," he said, urging the financial sector to reinforce IT security.
Hacking attacks have recently struck banks, savings banks, mutual finance institutions and credit finance companies across the board, while the financial investment and insurance sectors had until now reported no breaches. A personal data leak at Mirae Asset Life Insurance on Monday, followed by the incident at Daishin Securities, suggests the threat is spreading across the entire financial industry.
yuni@heraldcorp.com