LG Uplus is moving to proactively identify global security threats by partnering with a white-hat hacker platform to strengthen its vulnerability verification system.
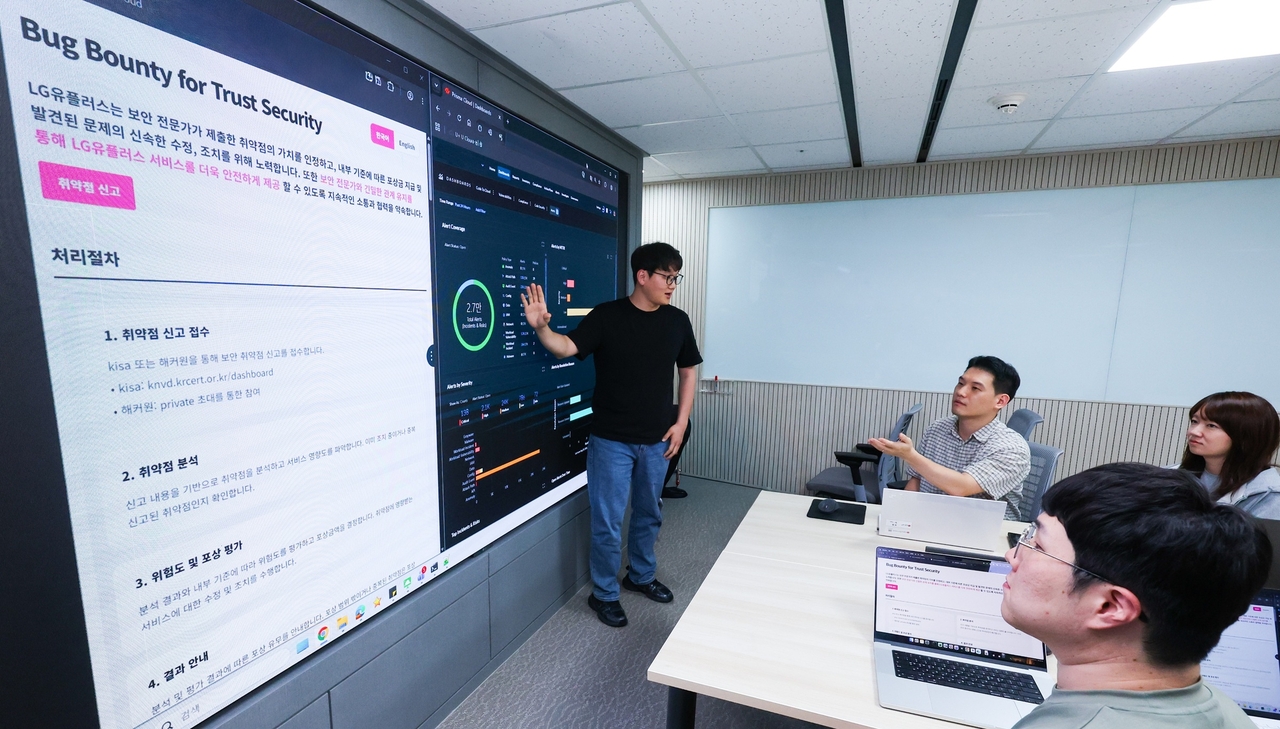
The company said Monday it is launching a global bug bounty program in partnership with HackerOne, the world's largest bug bounty platform. The initiative aims to uncover potential vulnerabilities that domestic security verification systems alone may struggle to detect, by tapping into a worldwide community of white-hat hackers.
The program covers all of LG Uplus's service areas, including mobile, internet and enterprise services.
A bug bounty is a system in which companies and organizations reward white-hat hackers who discover security vulnerabilities in their services and IT infrastructure. It allows companies to identify and address weaknesses early, building a more robust security environment.
The move comes as advances in AI have increased security threats — including new vulnerabilities, attack vectors and methods that hackers can exploit. Telecommunications services in particular are seeing growing exposure to overseas infrastructure through roaming, cloud and AI services.
HackerOne operates the world's largest bug bounty platform, with more than 2.4 million white-hat hackers participating globally. The platform has maintained long-standing partnerships with the US Department of Defense and numerous global technology companies.
The bug bounty program will operate as a private, invitation-only arrangement open exclusively to vetted global white-hat hackers. Reports from participants will be accepted on a continuous basis, with vulnerabilities swiftly analyzed and remediated alongside threat detection. Through this, LG Uplus plans to get ahead of potential security risks before they can be exploited.
The company also expects to build a vulnerability management system that meets global standards. While continuing to co-operate with the Korea Internet & Security Agency on its domestic bug bounty program, LG Uplus will run the HackerOne program separately, with the goal of uncovering previously undetected vulnerabilities and blind spots in its security management.
"As telecommunications services increasingly interface with overseas infrastructure, our goal is to proactively identify even the vulnerabilities we have yet to discover," said Hong Gwan-hee, chief information security officer at LG Uplus. "Through this, we will lead the way in building a safe and transparent security ecosystem and spreading a culture of responsible vulnerability management."
ko@heraldcorp.com